AI Scan governance is now an API problem: define the policy boundary before automating rollout
AI Scan governance is now an API problem: define the policy boundary before automating rollout
Campaign: PMS-daily-2026-11-13
Content ID: PMS-D20261113-ARTICLE-01
Revision: 1
State: draft for Quality Editor review
Destination: Ghost
A repository-security rollout can look like a small automation job: read a setting, change it across a group of repositories, and move on. That picture becomes misleading as soon as a central policy can constrain the change—or when enabling the setting is mistaken for actually running a scan.
GitHub’s November 13 announcement makes that distinction important. GitHub says its public-preview AI Scan controls now include a repository_scan setting in existing enablement endpoints, with organization- and repository-level operations available through a Representational State Transfer Application Programming Interface (REST API). In plain language, a REST API is an HTTP interface that software can use to read or change settings. GitHub also says organization settings can constrain repository behavior, an enterprise policy can cause a 422 response when enablement is attempted, enabling the setting does not start a scan, and on-demand scans consume Code Security AI credits. This feature does not support GitHub Enterprise Server. Source: GitHub Changelog, November 13, 2026
The useful question, then, is not “Can we automate this?” It is “Where is the policy boundary, what does each response tell us, and who owns the decision to run a scan?”
Start with the control plane
AI Scan is GitHub’s name for a repository scanning capability. The current announcement describes how its enablement setting can be managed; it does not establish detection quality, repository coverage, adoption, cost-effectiveness, or improved security.
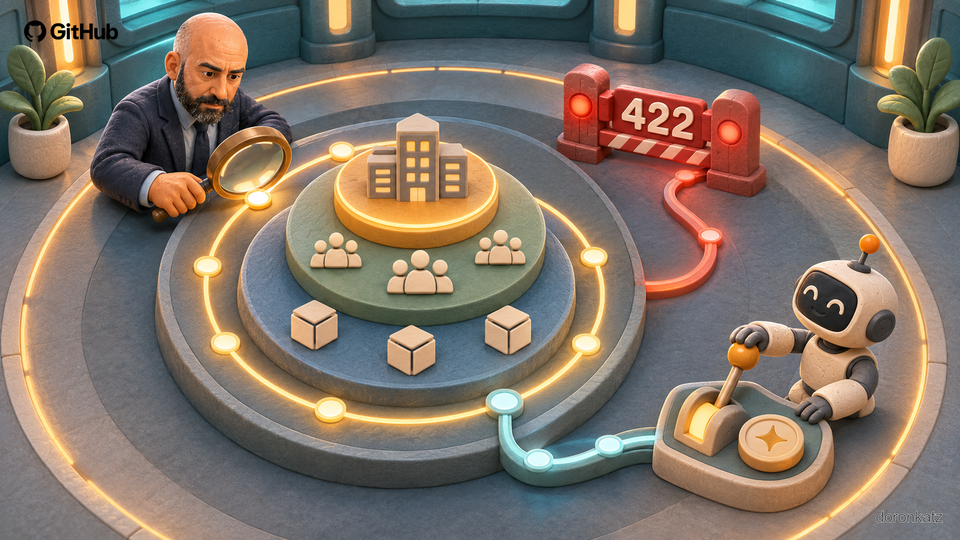
Treat the rollout as a control-plane decision. The control plane is the part of a system that determines who may change configuration and which rules apply. Here, the relevant policy boundary may sit at the enterprise, organization, or repository level. A repository owner can request a state without necessarily having authority to override a rule above it.
“Public preview” matters too. It means the feature is in an early-access state, so availability and behavior may be limited or change. Before writing automation, verify that the relevant account, plan, platform, and repositories can use the preview. Do not infer eligibility from the announcement alone.
What changed—and what did not
GitHub says the new repository_scan setting is part of existing AI Scan enablement endpoints and can be managed for organizations and repositories through scripts or infrastructure as code. Infrastructure as code means managing configuration through versioned, reviewable files and automation instead of relying only on manual clicks. Source: GitHub Changelog
That creates a practical automation surface, but it does not erase hierarchy. GitHub’s announcement says an organization setting can constrain repository behavior. It also documents a 422 response when an enterprise policy prevents enablement. A 422 in this specific path is governance evidence: the request reached a rule it could not satisfy. It is a prompt to inspect the policy and responsible owner, not a reason to search for a bypass.
The other critical distinction is between configuration and execution. GitHub says enabling the setting does not itself start a scan. A separate on-demand scan consumes Code Security AI credits. Keep those decisions separate in both the interface and the approval record.
A six-step rollout checklist
1. Confirm the supported surface
Record the hosting environment, account or plan eligibility, preview availability, and repositories in scope. GitHub says this API feature does not support GitHub Enterprise Server, so a mixed environment cannot be treated as one uniform rollout. This check prevents an unsupported surface from being mistaken for a permissions failure.
2. Map authority before changing state
Draw the chain from enterprise to organization to repository. For each level, name the policy owner, the operator allowed to read settings, and the operator allowed to request a change. This makes a later denial interpretable: you can ask whether the request conflicted with enterprise policy, organization configuration, or repository permissions.
3. Read before you write
Inventory the current organization and repository settings using read-only operations where permitted. Save the time, scope, actor, and result. A read-first pass exposes differences without creating them and gives reviewers a baseline for the proposed change.
4. Define expected denial and inheritance behavior
Before a write, document what should happen when a repository requests a state that a higher-level policy constrains. Verify current inheritance and opt-out semantics in GitHub’s live documentation for your environment; the announcement alone is not enough to describe every account’s behavior. If a documented policy-denied 422 occurs, preserve the request context and route the decision to the policy owner instead of retrying blindly.
5. Separate enablement from scan execution
Use two explicit fields in the change record:
- Setting enabled?
yes,no, orunchanged - Scan requested?
yesorno, with the approver responsible for Code Security AI credits
This small separation prevents a successful configuration response from being reported as a completed scan. It also keeps the credit decision visible instead of hiding it inside automation.
6. Make the test reversible and reviewable
If policy permits, choose a non-production or otherwise low-risk repository for a limited test. Record the requested state, previous state, response, reviewer, rollback path, and whether a scan was actually requested. Stop if scope, authority, preview eligibility, expected error behavior, or credit ownership is unresolved.
Worked example: an exception request meets organization policy
Consider a hypothetical platform team with an organization-level policy. A repository owner asks to enable AI Scan for one repository.
The operator first records the repository and organization in scope, confirms that the hosting surface supports the preview, and identifies the organization policy owner. A read-only check captures the current setting. The proposed decision record contains the actor, requested state, policy context, reviewer, and rollback path.
If the enablement request receives the policy-denied response described by GitHub, the operator does not retry with a different route. They attach the response to the decision record and ask the policy owner whether the organization rule should change. If the setting is eventually enabled, the record still says “scan requested: no” until a separate, approved action requests a scan. No result or security benefit is inferred from enablement alone.
This example is deliberately hypothetical. It does not claim a particular organization, cost, scan result, or outcome.
Common mistakes to avoid
One mistake is treating public preview as general availability. Another is assuming repository-level access overrides organization or enterprise policy. A third is reading an HTTP success response as proof that a scan ran. A fourth is treating scan credits as an unlimited implementation detail rather than an owned decision.
The biggest analytical mistake is claiming more than the source proves. GitHub’s announcement documents an API surface and specific behavior. It does not prove that enabling AI Scan improves security, that every repository is covered, or that the rollout will be cost-effective.
The practical decision rule
Proceed to a limited, reviewed control-plane test only when you can document five things: supported scope, authority at each policy level, preview eligibility, expected denial behavior, and ownership of the scan-credit decision.
If any of those is missing, stop at read-only inventory. Verify the live documentation and resolve the ownership gap before issuing a write. Automation should make the decision reproducible—not make the policy boundary easier to overlook.
Source
GITHUB-AI-SCAN-API-20261113: GitHub Changelog — Manage AI Scan for repositories using the REST API, November 13, 2026.
Member discussion